Introduction
Over the past decade, compliance functions have undergone significant transformation. Increasing regulatory expectations, evolving financial crime risks, and rapid technological advancement have driven financial institutions to strengthen their governance frameworks, enhance monitoring capabilities, and invest heavily in compliance infrastructure. Today, organisations routinely measure compliance performance through dashboards, key performance indicators (KPIs), key risk indicators (KRIs), monitoring programmes, training statistics, and management information presented to senior leadership.
These developments have undoubtedly improved oversight and accountability. However, they also raise an important question that receives far less attention: do these measures genuinely demonstrate that compliance is effective, or do they simply demonstrate that compliance activity has taken place?
This distinction is becoming increasingly important. Regulators no longer expect firms merely to demonstrate the existence of policies and controls. Instead, they increasingly focus on whether those controls achieve their intended outcomes. The Financial Conduct Authority (FCA) has consistently emphasised that firms must establish effective systems and controls proportionate to the nature, scale, and complexity of their business (FCA, 2023). Similarly, the Financial Action Task Force (FATF) has shifted global supervisory attention towards effectiveness, recognising that technical compliance alone provides only a partial assessment of an institution’s ability to manage financial crime risk (FATF, 2023).
From my perspective, many organisations continue to assess compliance performance primarily through operational activity rather than measurable risk reduction. Reports often demonstrate how much work has been completed, but provide far less evidence that financial crime risk has actually been mitigated. As regulatory expectations continue to evolve, distinguishing between compliance activity and compliance effectiveness may become one of the most significant challenges facing financial institutions.
The growth of performance measurement in compliance
Modern compliance functions generate an enormous volume of management information. Senior management and Boards receive regular reports covering training completion rates, customer due diligence reviews, transaction monitoring alerts, sanctions screening results, regulatory breaches, internal audit findings, policy reviews, and compliance monitoring outcomes. These metrics provide valuable oversight and support governance by enabling management to monitor operational performance.
The increased use of performance metrics reflects a broader shift towards data-driven governance. Institutions seek measurable indicators that demonstrate accountability, facilitate regulatory reporting, and support informed decision-making. In many respects, this represents positive progress. Quantitative reporting enables organisations to identify trends, allocate resources, and monitor whether compliance activities are being completed within expected timeframes.
However, the growing emphasis on measurement has also created an unintended consequence. Organisations increasingly measure what is easiest to count rather than what is most meaningful to understand.
For example, a compliance dashboard may report that:
- 98% of mandatory training has been completed;
- all scheduled compliance monitoring reviews have been conducted;
- customer due diligence reviews are completed within agreed service levels;
- transaction monitoring alerts have been reviewed within target timescales; and
- all required policies have undergone annual review.
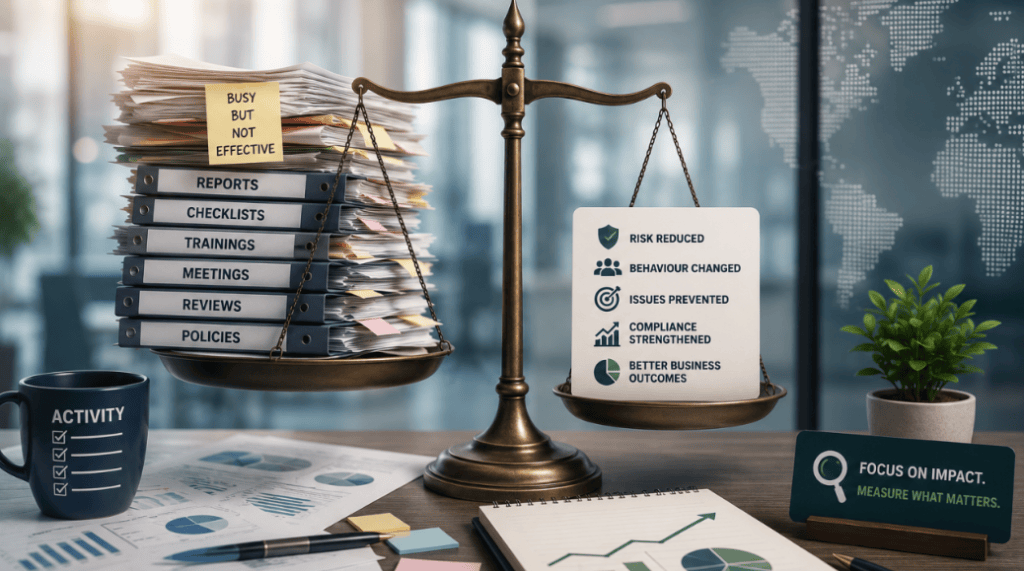
Individually, these measures demonstrate operational activity. Collectively, they create the appearance of a well-functioning compliance framework. Yet none of these metrics, in isolation, confirms whether financial crime risk has actually been reduced.
This distinction is critical. A compliance function can demonstrate exceptionally high levels of operational efficiency while still failing to identify emerging risks, detect suspicious activity, or influence risk-aware decision-making across the organisation.
When activity becomes a poor measure of effectiveness
One of the most significant challenges within compliance performance management is the tendency to confuse productivity with effectiveness. Although closely related, the two concepts are fundamentally different.
Activity measures demonstrate that specific tasks have been completed. Effectiveness measures demonstrate whether those activities achieved their intended objective.
This difference can be illustrated across several core compliance activities.
A high volume of transaction monitoring alerts reviewed does not necessarily indicate effective transaction monitoring. Excessive alert volumes may instead reflect poorly calibrated scenarios generating large numbers of false positives, reducing analyst capacity to investigate genuinely higher-risk activity.
Similarly, achieving 100 per cent completion of mandatory AML training does not necessarily demonstrate improved financial crime awareness. Training completion measures attendance, not understanding, judgement, or behavioural change.
Even low numbers of reported regulatory breaches should be interpreted carefully. While they may indicate a strong control environment, they may equally suggest weaknesses in issue identification, escalation, or reporting processes.
In practice, these distinctions are often overlooked because activity is relatively easy to measure. Compliance effectiveness, by contrast, is considerably more difficult to quantify.
From my experience, organisations frequently place considerable emphasis on reporting operational statistics to governance committees while giving comparatively less attention to whether those statistics genuinely reflect risk management outcomes. As a result, management reporting can sometimes provide reassurance without necessarily providing assurance.
The Basel Committee on Banking Supervision has repeatedly emphasised that effective risk management depends not only upon robust governance arrangements but also upon the quality of information supporting management decisions (BCBS, 2021). Where performance indicators fail to reflect actual risk exposure, governance itself becomes less effective.
The illusion of strong compliance performance
Perhaps the greatest danger associated with activity-based measurement is the creation of a false sense of confidence.
Within many organisations, compliance dashboards dominated by green indicators naturally create reassurance. Monitoring programmes have been completed. Mandatory training targets have been achieved. Policies remain up to date. Internal reporting deadlines have been met. From a governance perspective, these outcomes appear positive.
However, financial crime rarely develops because policies have not been reviewed or because monitoring reports were submitted late.
More commonly, failures emerge because underlying risks evolve faster than existing controls.
Customer behaviour changes. Criminal methodologies become more sophisticated. Data quality deteriorates. Operational pressures influence decision-making. System configurations gradually become outdated. Individually these issues may appear relatively minor. Collectively, they can significantly weaken the effectiveness of a compliance framework despite consistently positive performance reports.
This demonstrates an important principle. Strong compliance reporting does not always indicate strong compliance performance.
Rather, it may simply indicate that organisations have become highly effective at measuring operational activity while overlooking whether controls continue to operate effectively under changing risk conditions.
In today’s increasingly complex regulatory environment, the question should therefore no longer be “Have we completed the required compliance activities?” Instead, it should become “Can we demonstrate that those activities have genuinely reduced financial crime risk?”
Measuring what really matters
If activity alone is insufficient to demonstrate compliance effectiveness, the next question becomes what organisations should measure instead.
Rather than focusing exclusively on operational outputs, institutions should increasingly assess whether controls are achieving their intended objectives. This requires a shift from measuring efficiency to evaluating effectiveness.
For example, instead of simply reporting the number of transaction monitoring alerts reviewed, organisations should consider whether alert calibration is successfully identifying genuinely suspicious activity. Rather than measuring how many customer due diligence reviews have been completed, greater emphasis should be placed on whether customer risk assessments remain accurate as customer behaviour evolves.
Similarly, compliance monitoring programmes should extend beyond confirming whether controls exist. They should assess whether those controls continue to operate effectively under changing business conditions.
One area that deserves greater attention is the analysis of recurring findings. A compliance issue that repeatedly appears during monitoring, internal audit, or regulatory review often indicates that the underlying root cause has not been addressed. Closing an issue may satisfy governance reporting requirements, but unless the fundamental weakness is resolved, the same risk is likely to re-emerge.
Root cause analysis therefore becomes an important indicator of compliance maturity. Organisations that consistently investigate why control failures occur, rather than simply documenting that they occurred, are better positioned to strengthen their control environment over time.
From my perspective, the most effective compliance functions place greater emphasis on continuous learning than on statistical reporting. Every incident, investigation, audit finding, or near miss represents an opportunity to improve the framework rather than simply complete another governance action.
From compliance reporting to compliance assurance
An equally important distinction exists between reporting compliance activity and providing genuine assurance over compliance effectiveness.
Governance committees frequently receive extensive management information containing performance indicators, monitoring results, regulatory updates, and operational statistics. While these reports are valuable, they often focus on what has happened rather than whether the organisation remains adequately protected against emerging risks.
True assurance requires a more challenging perspective.
Instead of asking whether monitoring was completed, organisations should ask whether monitoring tested the areas presenting the highest levels of financial crime risk.
Instead of asking whether policies have been reviewed, they should consider whether those policies continue to reflect current business activities, technological developments, and evolving criminal methodologies.
Similarly, reporting that no significant issues were identified during a monitoring review should not automatically be interpreted as evidence of an effective control environment. It may equally indicate that monitoring activities were insufficiently targeted or that emerging risks remain undetected.
This reflects a broader shift within financial regulation. Increasingly, supervisory authorities are interested not only in the existence of governance arrangements but also in the quality of challenge provided by Boards, senior management, and control functions.
The Financial Conduct Authority has consistently emphasised that firms should maintain effective governance arrangements supported by robust systems and controls capable of identifying, assessing, managing, and monitoring financial crime risk (FCA, 2023). These expectations extend beyond documentation and require firms to demonstrate that governance arrangements remain effective in practice.
Consequently, compliance reporting should increasingly support informed decision-making rather than simply provide operational updates. Reports should encourage challenge, identify uncertainty, and highlight emerging risks rather than merely confirm that routine activities have been completed.
Building an outcome-focused compliance framework
Developing a genuinely effective compliance framework requires a shift in organisational mindset.
Compliance should no longer be viewed solely as a function responsible for completing regulatory obligations. Instead, it should be recognised as an integral component of enterprise risk management, supporting informed business decisions while protecting the integrity of the organisation.
Achieving this requires several practical changes.
First, performance indicators should incorporate measures of control quality rather than relying exclusively on activity volumes. Quality assurance reviews, recurring findings, investigation outcomes, and root cause analysis often provide more meaningful insight than operational statistics alone.
Second, organisations should strengthen feedback mechanisms across the three lines of defence. Lessons identified through investigations, compliance monitoring, internal audit, operational incidents, and regulatory reviews should be systematically incorporated into policy development, system enhancement, and staff training. Continuous improvement should become an embedded characteristic of the compliance framework rather than a reactive response to regulatory criticism.
Third, greater attention should be given to behavioural indicators. Compliance effectiveness ultimately depends on how individuals identify, escalate, and manage risk within day-to-day operations. Measures such as escalation quality, decision consistency, challenge provided during governance discussions, and ownership of risk by the first line may provide stronger indicators of organisational resilience than numerical activity alone.
Finally, senior management should recognise that compliance performance cannot be measured solely through historical reporting. Effective governance requires organisations to anticipate emerging risks, challenge existing assumptions, and continually evaluate whether current controls remain appropriate within an evolving financial crime landscape.
This approach aligns closely with the broader direction of international regulatory expectations, which increasingly emphasise outcomes, resilience, and continuous improvement rather than technical compliance alone.
Conclusion
Compliance functions have become increasingly sophisticated. Financial institutions now possess more data, more technology, and more governance information than at any point in their history. Yet the ability to measure compliance activity has advanced more rapidly than the ability to measure compliance effectiveness.
This distinction is becoming increasingly significant.
High training completion rates, timely monitoring reviews, updated policies, and positive dashboard reporting undoubtedly demonstrate that important compliance activities are taking place. However, they do not necessarily demonstrate that financial crime risk is being effectively identified, managed, or reduced.
As financial crime continues to evolve and regulatory expectations become increasingly outcome focused, organisations must reconsider how they evaluate compliance performance. Measuring what is easy should not replace measuring what is important.
From my perspective, the future of compliance lies not in producing more management information but in generating more meaningful assurance. Institutions that critically evaluate the effectiveness of their controls, continuously challenge their assumptions, and use performance measurement to drive genuine improvement will be better positioned to respond to evolving financial crime risks and increasing regulatory scrutiny.
Ultimately, compliance should not be judged by the quantity of activity completed but by its ability to influence behaviour, strengthen governance, and reduce risk. In an environment where financial crime methodologies continue to adapt, demonstrating effectiveness may become the most important compliance metric of all.
References
Basel Committee on Banking Supervision (BCBS) (2021) Principles for Operational Resilience. Basel: Bank for International Settlements.
European Banking Authority (EBA) (2021) Guidelines on ML/TF Risk Factors under Directive (EU) 2015/849. Paris: European Banking Authority.
Financial Action Task Force (FATF) (2023) International Standards on Combating Money Laundering and the Financing of Terrorism & Proliferation (The FATF Recommendations). Paris: FATF.
Financial Conduct Authority (FCA) (2023) Financial Crime Guide: A Firm’s Guide to Countering Financial Crime Risks. London: FCA.
Institute of Internal Auditors (IIA) (2024) Global Internal Audit Standards. Lake Mary, FL: The Institute of Internal Auditors.
International Organization for Standardization (ISO) (2018) ISO 31000:2018 Risk Management – Guidelines. Geneva: ISO.
This article is also available on LinkedIn for wider readership.


Leave a comment